What it is
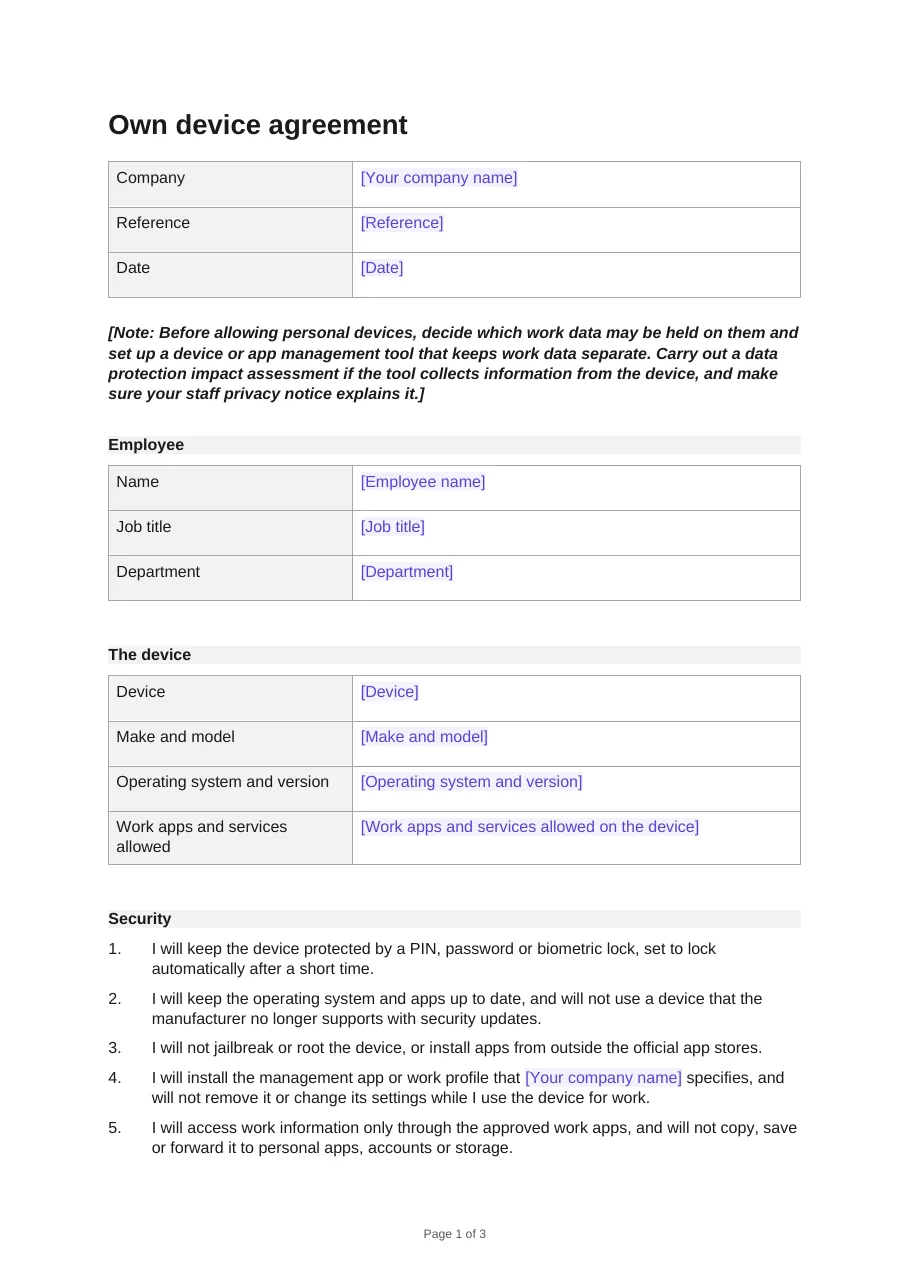
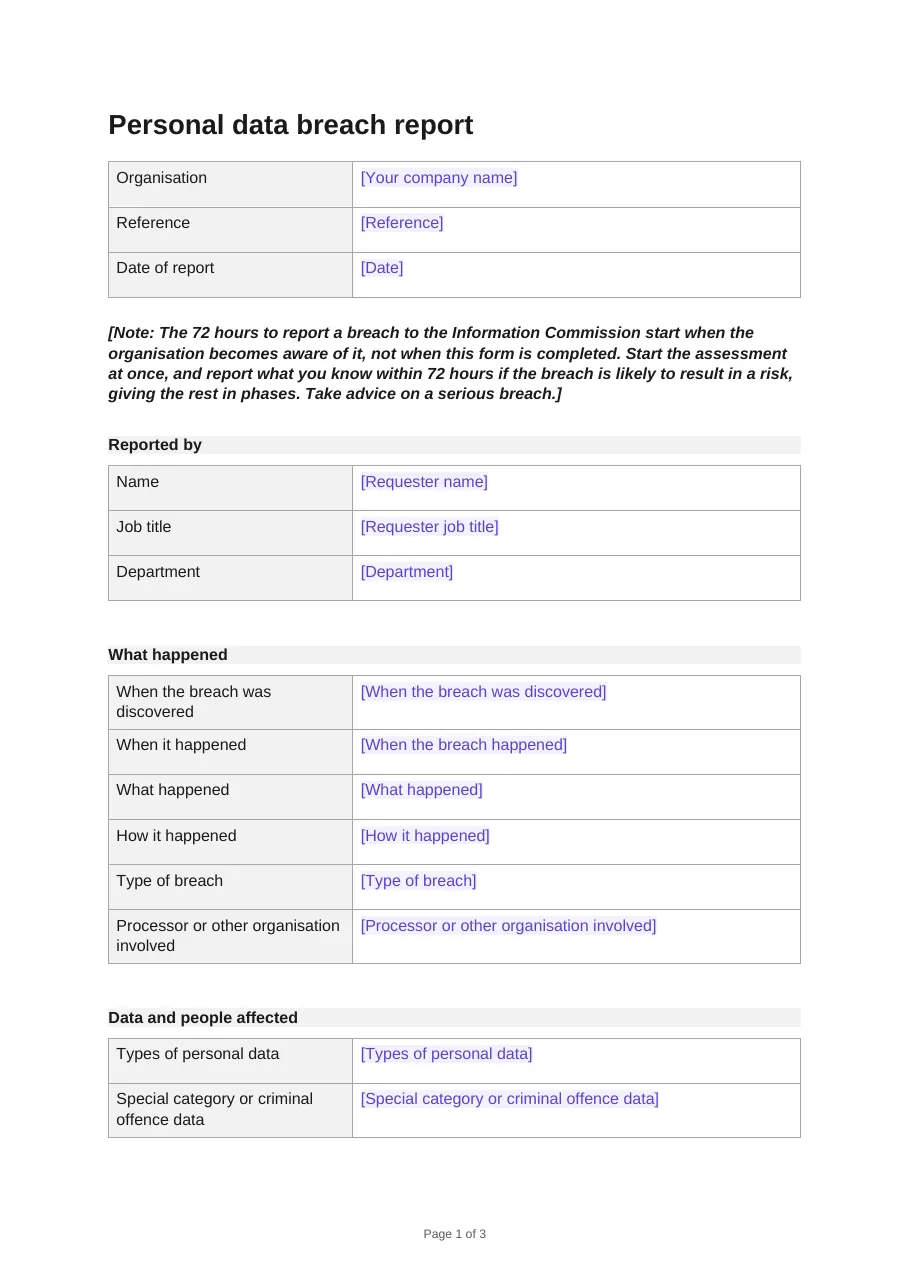
A data breach report records a personal data breach: what happened, when it was discovered, the data and people affected, what was done to contain it, the risk to the people concerned, and the decision on whether to report it to the Information Commission and tell those people. UK GDPR requires you to keep a record of every breach, including those you do not report.
How it works
The person who found or is handling the breach records what happened, the data and people affected, the action taken and the likely consequences, and signs. The approver, usually your data protection officer or a director, assesses the risk, records whether the Information Commission and the people affected were told and why, sets the follow-up actions and signs.
What you fill in
- Department
Sending it with Sign2Approve
In Documents, it comes with who signs, in what order, and what each person fills in already set. The order is a suggestion: change it before you send. Anyone can decline with a reason; you correct a copy and send that as the next version, and the declined one is kept. Once everyone has signed, the document is sealed with a completion certificate, and everyone gets a copy.